It is, at least, intriguing to follow the news of the Sony Pictures hack. The massive leakage underlines, once again, how security procedures are neglected, and how data protection is taken for granted. Passwords for the entirety of the company’s intranet? Accessed from an unencrypted folder. Final cuts for the company’s main films? Available for a multitude of employees without the need to know. Medical records and other personal information about the workforce? Placed within the boundaries of a globally accessed network. It is amazing to notice that no scandals have happened before. Steve Jobs is often quoted as saying something like: “Real IT guys basically only exist inside IT companies”. Realising the ignominious failure of Sony’s computer geeks, one cannot help but agree to him.
But that’s not all of it. The hacking group so-called “Guardians of Peace” has also exposed Sony as an object of ridicule. Apparently, the filmmaker’s chief operators conduct their daily activities by harshly offending their co-workers — most notably, calling Angelina Jolie “a minimally talented spoiled brat”, and characterising Leonardo DiCaprio’s professional behaviour as “despicable”. They have also been accused of making racist remarks about Barack Obama, citing films that had been starred by Black Americans. All this behind the veil of secrecy provided by email servers. Unfortunately for Sony Pictures, these messages were decrypted, read, and globally shared.
But that’s not all of it. A scathing critique of globalisation lies in the ever-growing power gap between multinational corporations and other entities (e.g., nation states). MNCs are simply getting too strong. Yet we have lived enough to watch Sony Pictures bend to the wishes of an outlaw gang of hackers. True, The Interview was eventually released — both physically and digitally. On the other hand, let’s take a look at how this film found its way towards its audience. No big chain of movie theatres has agreed to exhibit it, while, on the Internet, as of today, only major enterprises such as Google have ceded space to it. Not even Apple was disposed to expose its iTunes software to the risk of being hacked. In the end, supposedly North Korean-backed operatives were able to disrupt an entire infrastructure of Hollywood, justifying their acts by criticising The Interview.
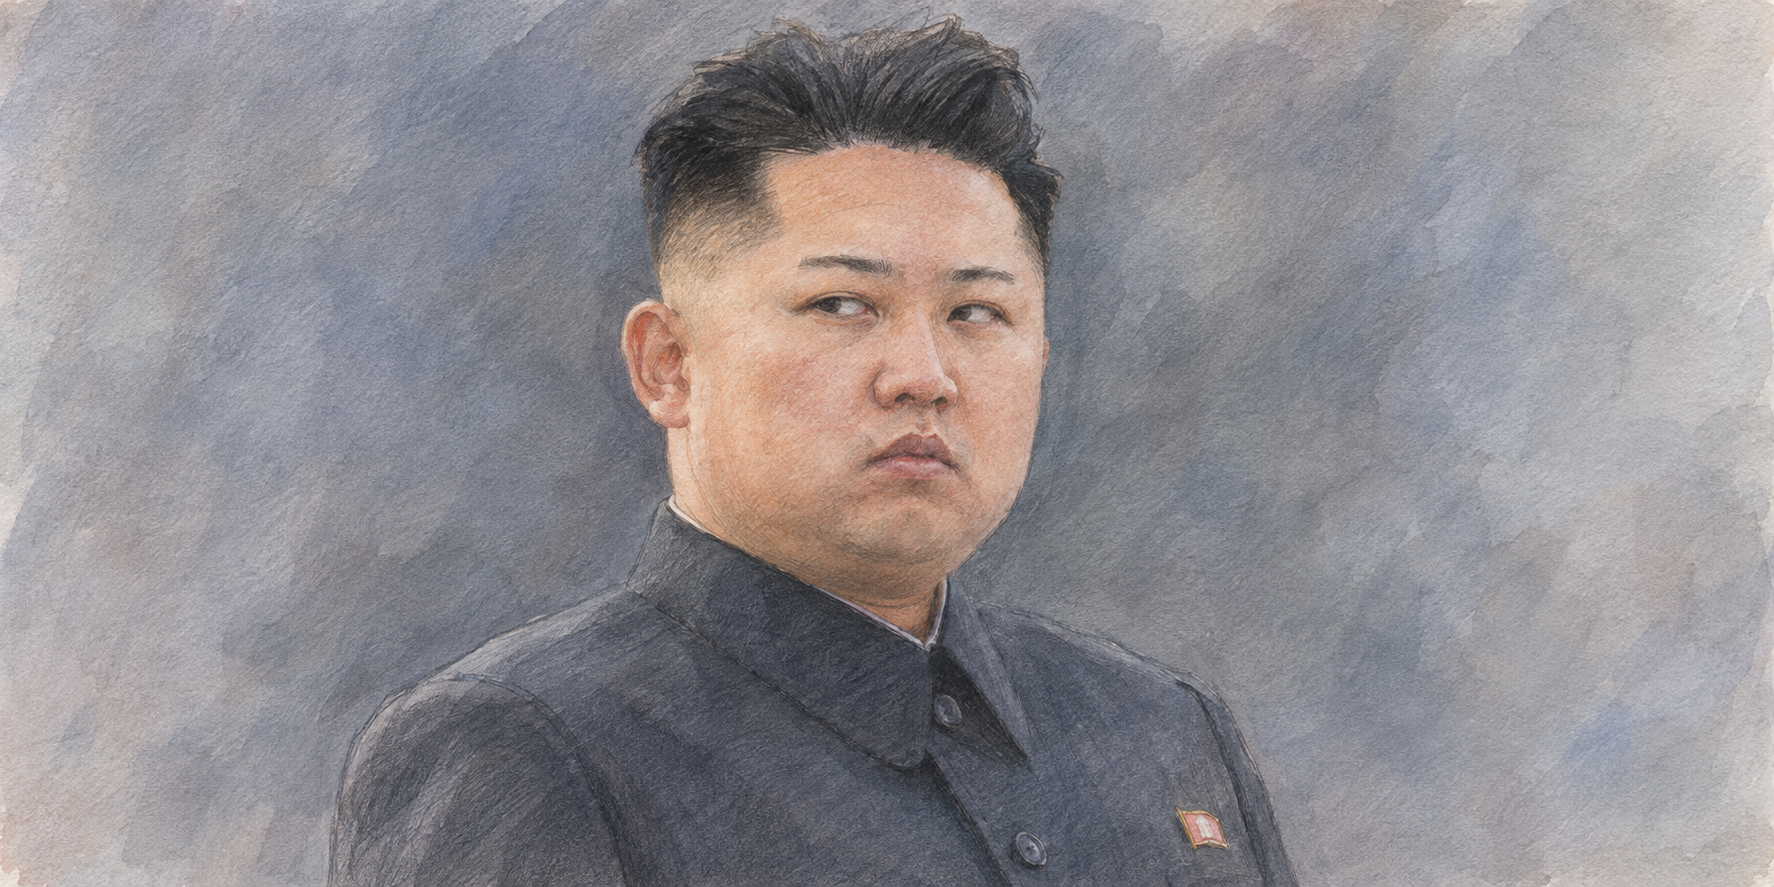
But that’s not all of it. The “Guardians of Peace” might be terrifyingly evil (they did threaten attacks similar to “9/11” in case the film was ever released), but they have a point. Sony Pictures got itself in the midst of this mess precisely because it fumbled when trying to find a good premise for its comedy (?) film. A plot that alludes to the murder of an active head of state — no matter if it is Angela Merkel or Kim Jong-un — is sure to set off a few sparks. Of course, we all probably know the controversies involving Jong-un’s mandate over North Korea: forced-labour fields, torture chambers, unequalled censure, warmongering rhetoric, illegitimate elections, and so forth. Nevertheless, international conspiracy and political assassinations aren’t (or, in fact, shouldn’t be) part of the sovereign-states-system playbook. Attempting to do such things is quite troubling; inciting the world to favour them is even more.
Perhaps, had Sony Pictures never envisaged conceiving The Interview, the company could have escaped facing the consequences of its negligence with regards to data protection, and of its employees’ carelessness when chatting through email treads. Much to Sony’s disgust, this option is no longer available. It has been (exemplary?) hacked, and its reputation and actual value ended up being severely damaged — it is not everyday that private businesses get to be a “matter of national security”. In the aftermath of this, I believe filmmakers will think twice before defining their plots and structuring their computer systems — in fact, I would argue that, as a whole, global forms will strive to become more security-conscious. There are certain issues about which one cannot be joking around, and that’s it.
Originally published on thimabi.wordpress.com.